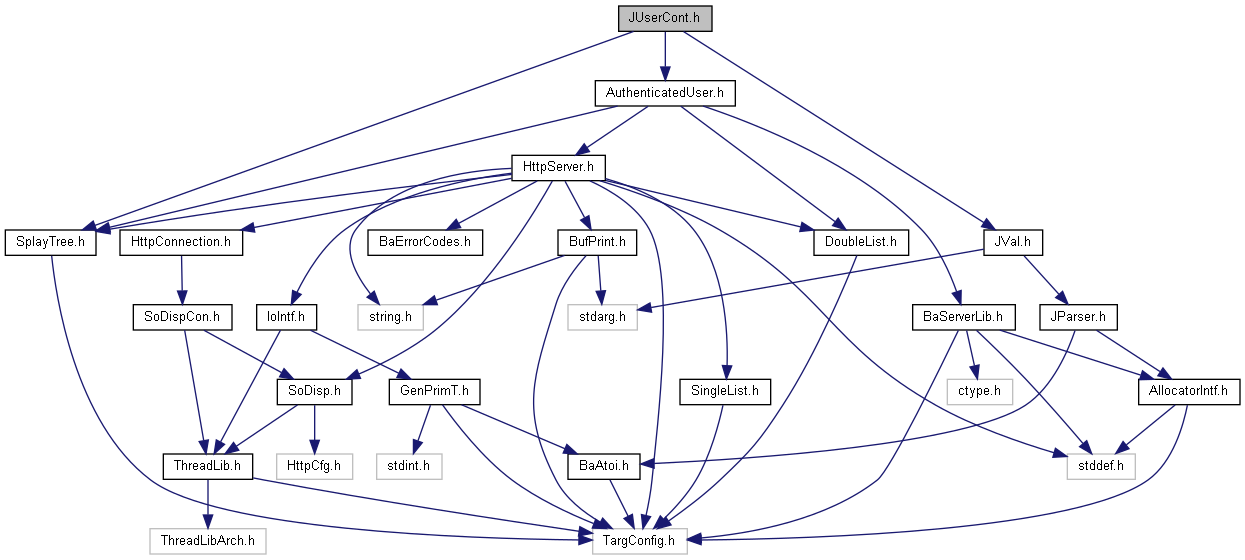
Go to the source code of this file.
Classes | |
| struct | JUserCont |
| User database implementing UserIntf, loaded from a parsed JSON object. More... | |
Typedefs | |
| typedef JUserCont | JUserCont |
| User database implementing UserIntf, loaded from a parsed JSON object. More... | |
Functions | |
| BA_API void | JUserCont_constructor (JUserCont *o, AllocatorIntf *alloc) |
| Initialize a user database. More... | |
| BA_API void | JUserCont_destructor (JUserCont *o) |
| Release all users and role mappings. More... | |
| BA_API void | JUserCont_setUserDb (JUserCont *o, JVal *usersVal, JErr *err) |
| Replace the user database without rollback. More... | |
Typedef Documentation
◆ JUserCont
User database implementing UserIntf, loaded from a parsed JSON object.
Object member names are usernames. Each user requires pwd and roles:
pwd is a string, or an array whose first string is a 32-character HA1 value for the MD5 authentication variant. The remaining array elements are not used. roles is an array of role-name strings; an empty array or empty object means no roles. In JConstrCont, users without roles have super-user access.
Optional maxUsers (also accepted as maxusers) is an integer, default 5, clamped to 0..65535; zero omits the user. inactive is a nonnegative integer timeout in seconds, default zero; negative values become zero. recycle is a boolean, default FALSE. Missing or wrong-type optional values use defaults. Passwords longer than 98 bytes are stored but cannot be returned through the current AuthInfo password buffer, so authentication will fail for that user.
Updates replace the user list without rollback; role-name mappings persist until destruction. Serialize database updates with readers and authorizers.
Function Documentation
◆ JUserCont_constructor()
| BA_API void JUserCont_constructor | ( | JUserCont * | o, |
| AllocatorIntf * | alloc | ||
| ) |
Initialize a user database.
- Parameters
-
[out] o Caller-owned storage. [in] alloc Borrowed allocator, or NULL for the default allocator.
◆ JUserCont_destructor()
| BA_API void JUserCont_destructor | ( | JUserCont * | o | ) |
Release all users and role mappings.
- Parameters
-
[in,out] o Initialized database, no longer referenced by authenticators or authorizers. Does not free the allocator itself.
◆ JUserCont_setUserDb()
Replace the user database without rollback.
- Parameters
-
[in,out] o Initialized database. [in] usersVal Parsed JSON object; see JUserCont::setUserDb. [in,out] err Required initialized JErr receiving reported failures.